Workload architecture
Landing zones designed for your mix of containers (AKS), VMs, managed databases and serverless, right-sized from day one.
Managed Azure
Certified engineers design, migrate, run and optimise your production workloads on Azure (containers, VMs, databases and serverless) connected through enterprise-grade networking with ExpressRoute, Private Link and global load balancing, 24/7.
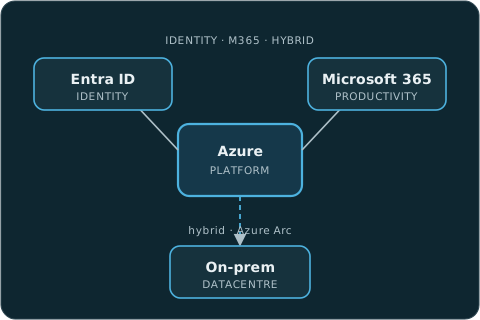
Azure gives you a global backbone with 60+ regions, sub-millisecond cross-zone latency, and networking primitives that rival a private WAN: ExpressRoute, VNet peering, Azure Front Door, Private Link. nFuse designs your Azure landing zone around the workloads you actually run and the connectivity they need, then operates it 24/7 so your team focuses on shipping, not infrastructure.
What we manage on Azure
Landing zones designed for your mix of containers (AKS), VMs, managed databases and serverless, right-sized from day one.
Hub-spoke VNets, ExpressRoute circuits, Azure Firewall and Private Link deliver secure, low-latency connectivity between workloads, on-prem and other clouds.
Site-to-site VPN, ExpressRoute Global Reach and Azure Arc extend one control plane to on-prem and third-party cloud workloads.
Azure Front Door, Traffic Manager and Application Gateway route traffic to the closest healthy endpoint: fast for users, resilient for you.
Right-sizing, reservations and savings plans keep your Azure spend reflecting actual workload demand, reviewed monthly.
Network Security Groups, DDoS Protection, Defender for Cloud and policy guardrails baked into every deployment.
Workload architecture
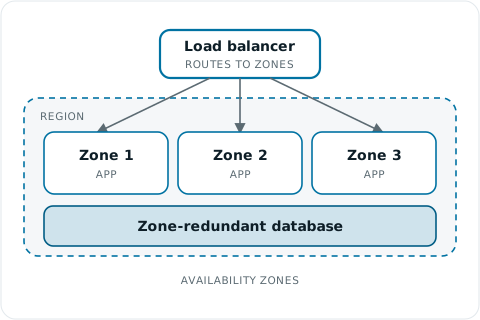
Certified architects design Azure landing zones with availability-zone redundancy, hub-spoke networking and workload isolation, so a single zone or fault never takes your production traffic down.
Automation & IaC
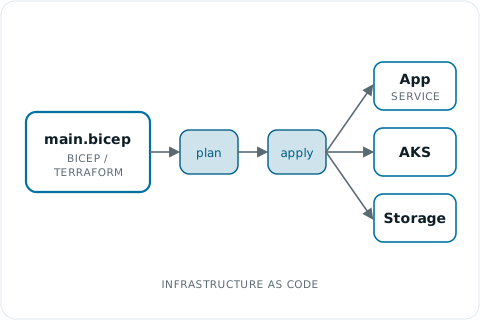
Every landing zone, network rule and workload config is defined in Bicep and Terraform, version-controlled and reproducible. One commit plans, reviews and applies the same way to dev, test and production.
Security in the loop
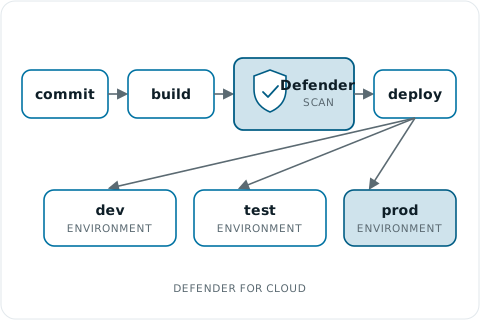
NSGs, Azure Firewall policies, Private Link and DDoS Protection form the perimeter; Defender for Cloud and policy guardrails ensure every workload deploys within those boundaries.
What you get
AKS clusters, VM scale sets and serverless functions auto-scale to demand, with no over-provisioning and no downtime.
ExpressRoute, Private Link and Front Door keep latency low and traffic off the public internet where it matters.
One control plane for Azure, on-prem and other clouds: consistent policy, single pane of glass.
Architecture, networking, operations and security from one team, one number to call.
FAQ
Anything from containerised microservices on AKS to legacy VMs, managed SQL databases, serverless functions and data pipelines. We design the landing zone around the workload, not the other way around.
Typically via ExpressRoute for private, low-latency connectivity, or site-to-site VPN for smaller footprints. We design hub-spoke topologies with Private Link so internal traffic never touches the public internet.
Yes. We assess, plan and execute migrations: lift-and-shift for quick wins, re-platform for long-term gains, with minimal disruption and a tested rollback path.
Yes. Right-sizing, reserved instances, savings plans and workload scheduling are part of the service, reviewed monthly alongside performance and security.